Emfirge maps your live cloud infrastructure, traces every path an attacker can take, and ships the fix as a Terraform PR. No agents. No guessing. Real infra, analyzed.
Enterprise-grade cloud security. Free during beta.
A read-only role. A cartography pass. A pull request. Live in production in under two minutes, with nothing to babysit.
One CloudFormation stack. No credentials stored. The agent never sees write access, to anything, ever.
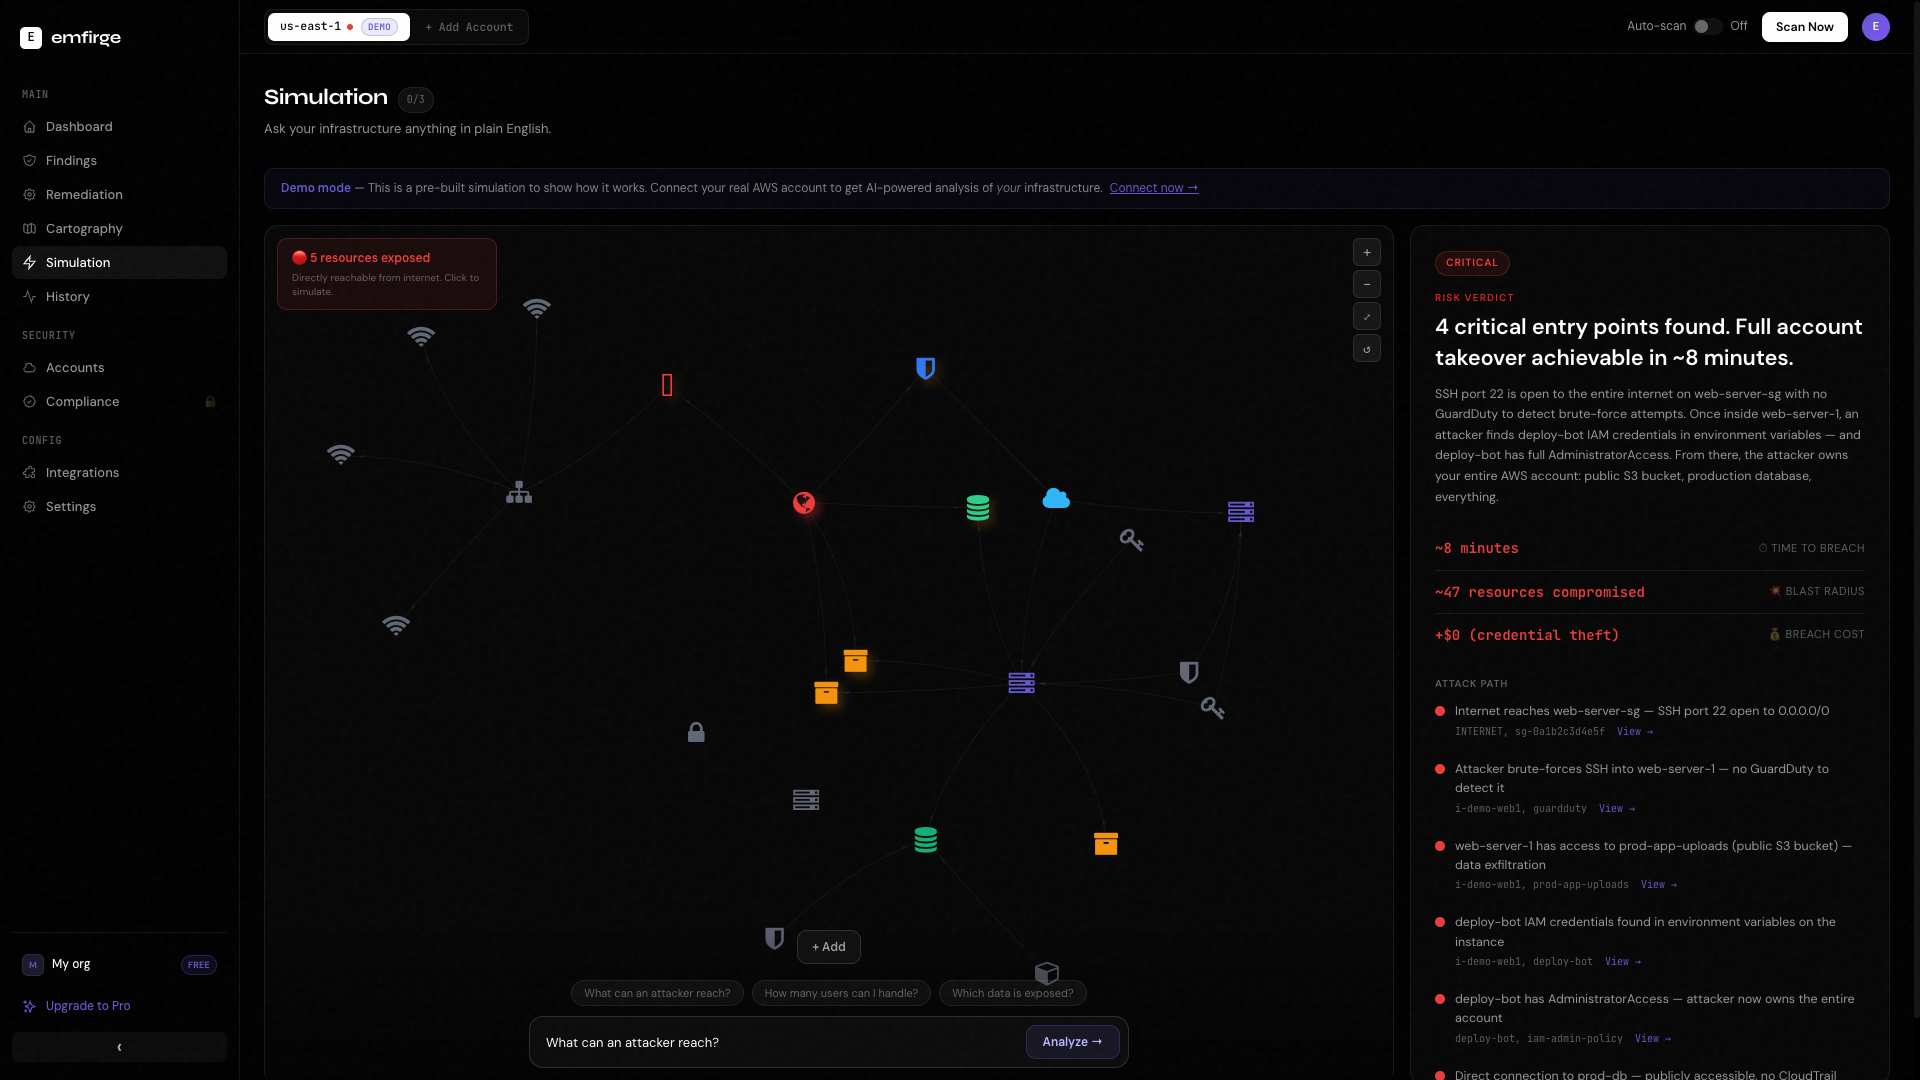
The agent traces every edge from the internet to your data. 18+ services. One graph. One redline path per finding.
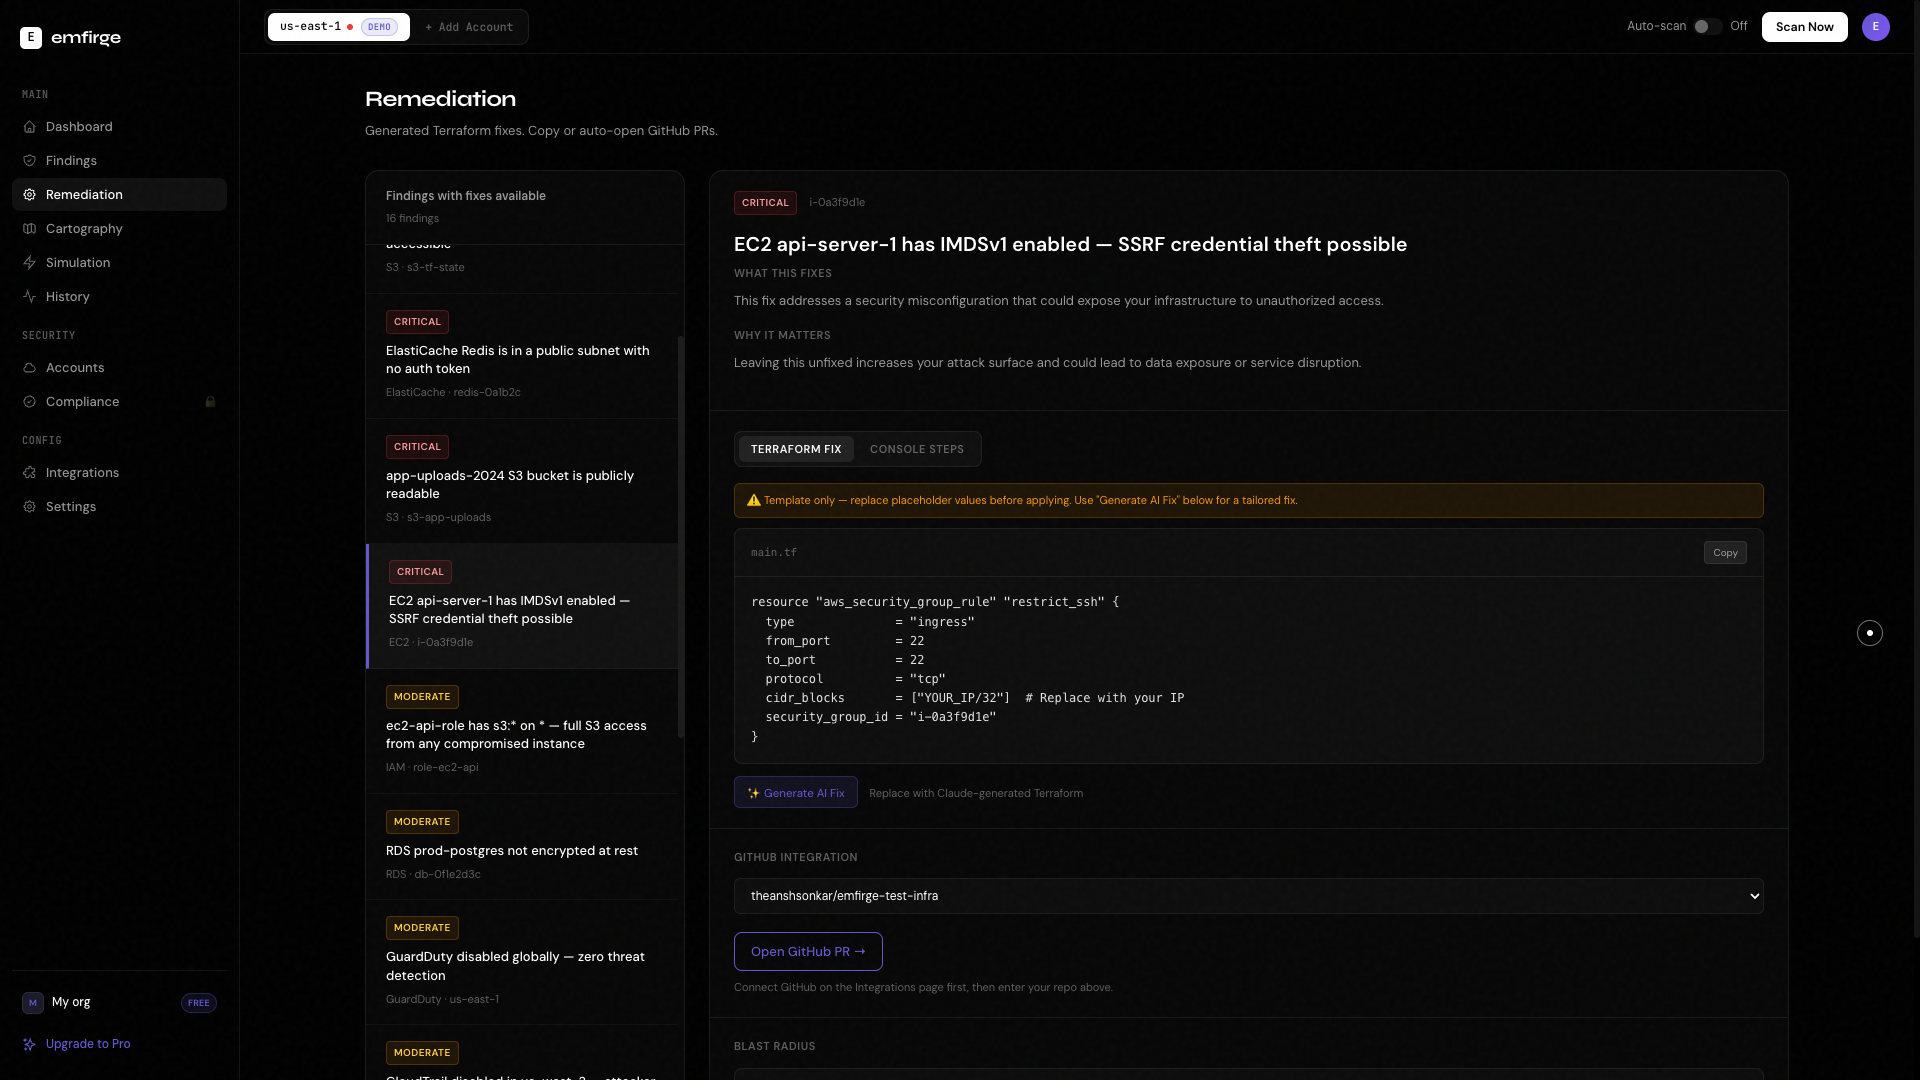
The agent writes HCL, opens a branch, links the finding. You review and merge. Production state never changes without you.
Pick a component type, configure it, hit Simulate. Emfirge shows the exact findings, risk score delta, and toxic combinations before the resource exists.
You see the new findings, the risk delta, the toxic combinations introduced, and the recommended remediation. All in the same graph.
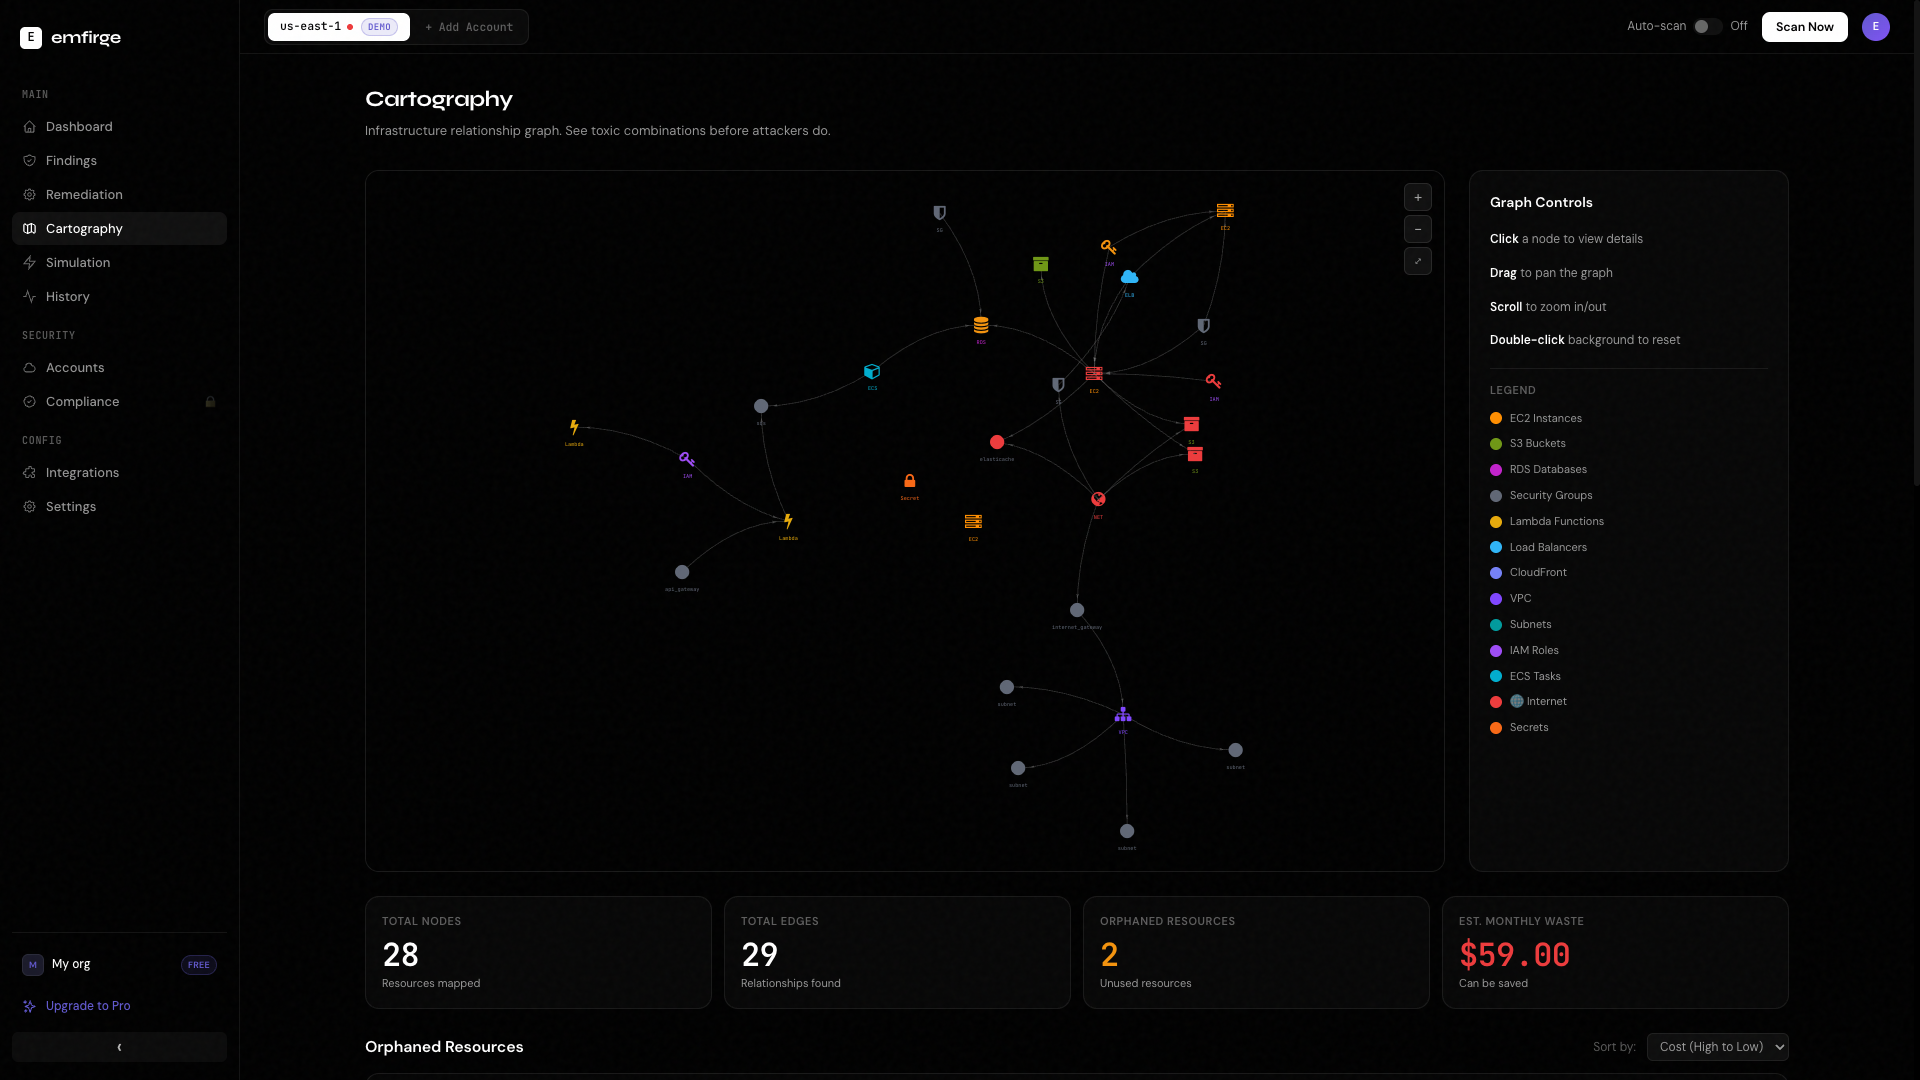
Emfirge maps 18+ cloud services in parallel, then renders the relationships as a graph. Not a list of misconfigurations. A topology. You can see exactly which resource is one hop from public.
Every edge is queryable. Every node carries its findings, its IAM, and its blast radius.
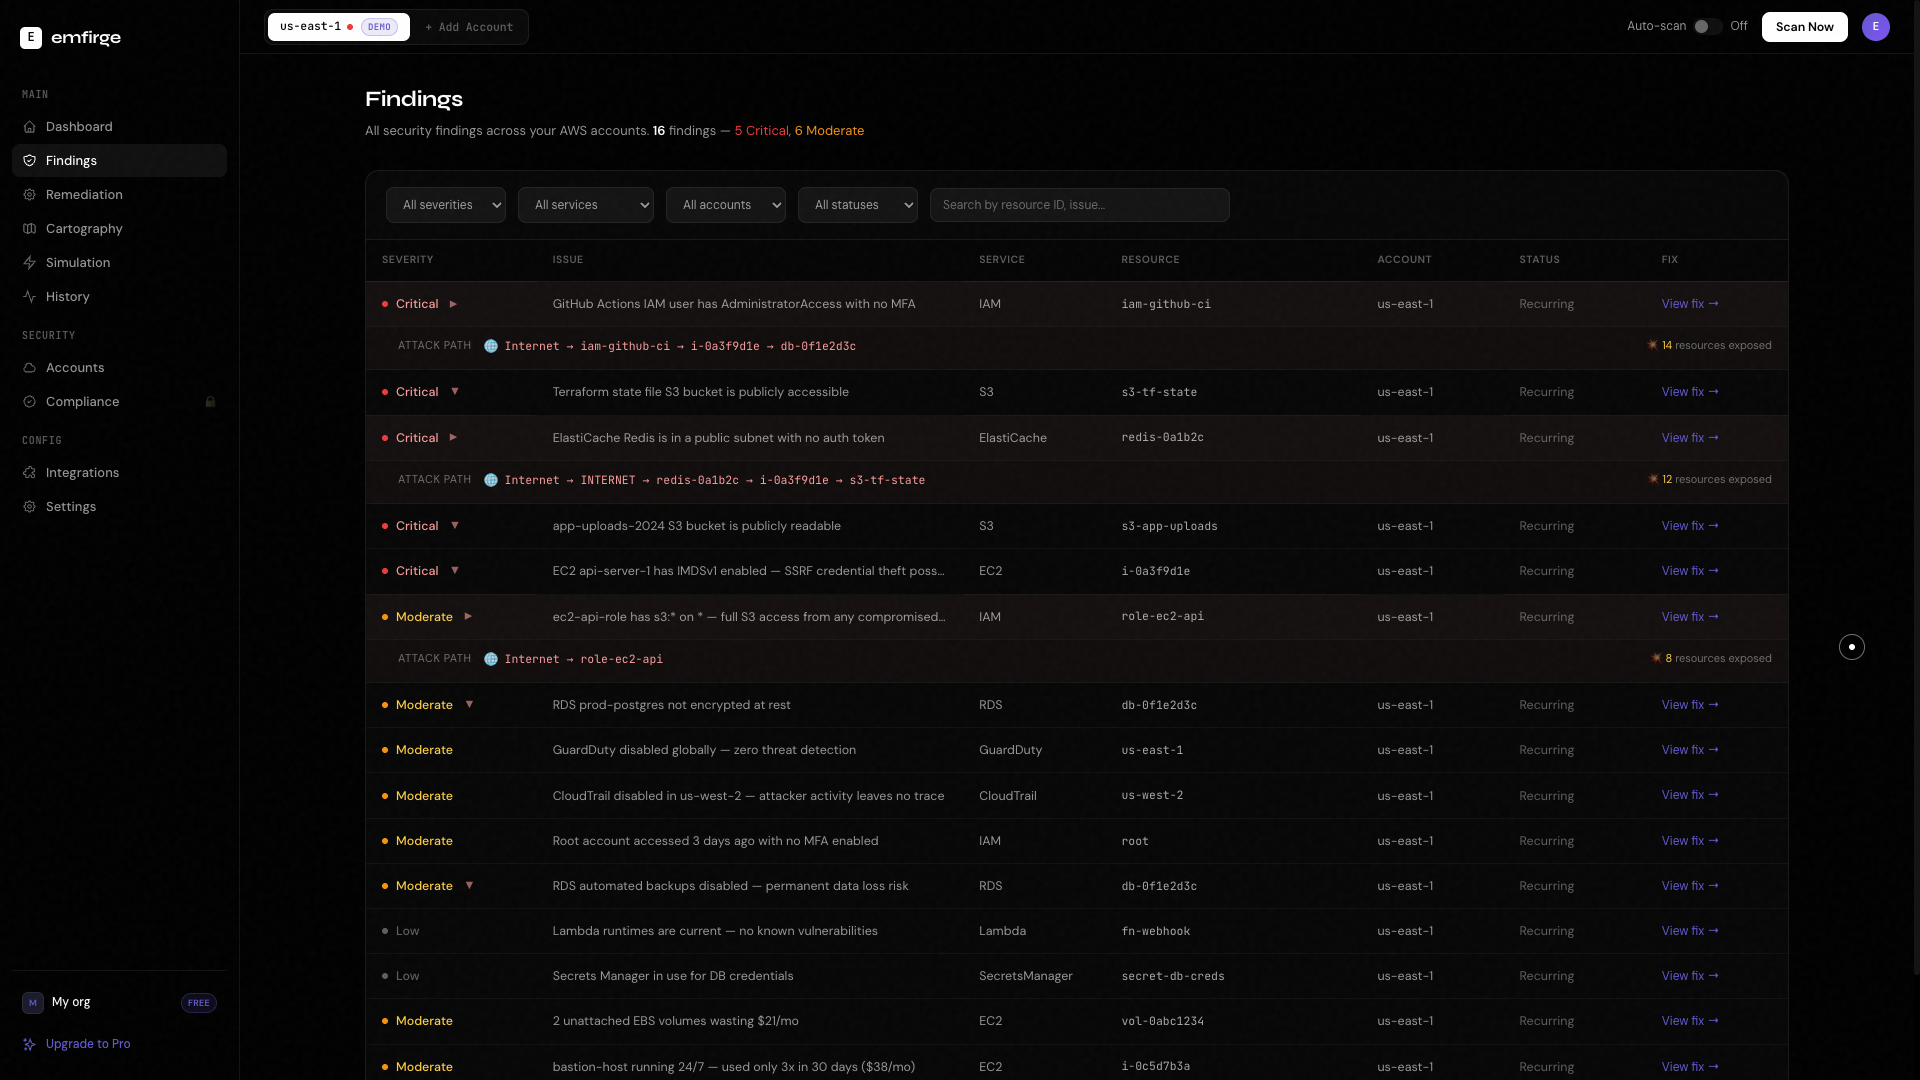
Other tools hand you a 4,000-line CSV. emfirge ranks risk by reachability, what an attacker can actually do from the internet, mapped to MITRE ATT&CK techniques.
Critical first. Noise last. With the resource graph behind every claim.
Emfirge writes the HCL, opens the PR on a feature branch, links the finding, and waits for your review. Never pushes to main. Never touches production directly.
You merge what you trust. The graph updates the moment the change lands.
Every finding Emfirge surfaces is a complete dossier, not a line item. Here's a real one, anonymized: a public ALB with overly-permissive ingress, fronting an EC2 instance whose IAM role can read the production database secret.
internet-reachable EC2
+ permissive SG (0.0.0.0/0)
+ instance role with secrets:GetSecretValue
= direct path from public to prod credentials
Built for companies with a CISO, a procurement team, and a security committee.
Built for the engineer who owns infra and security.